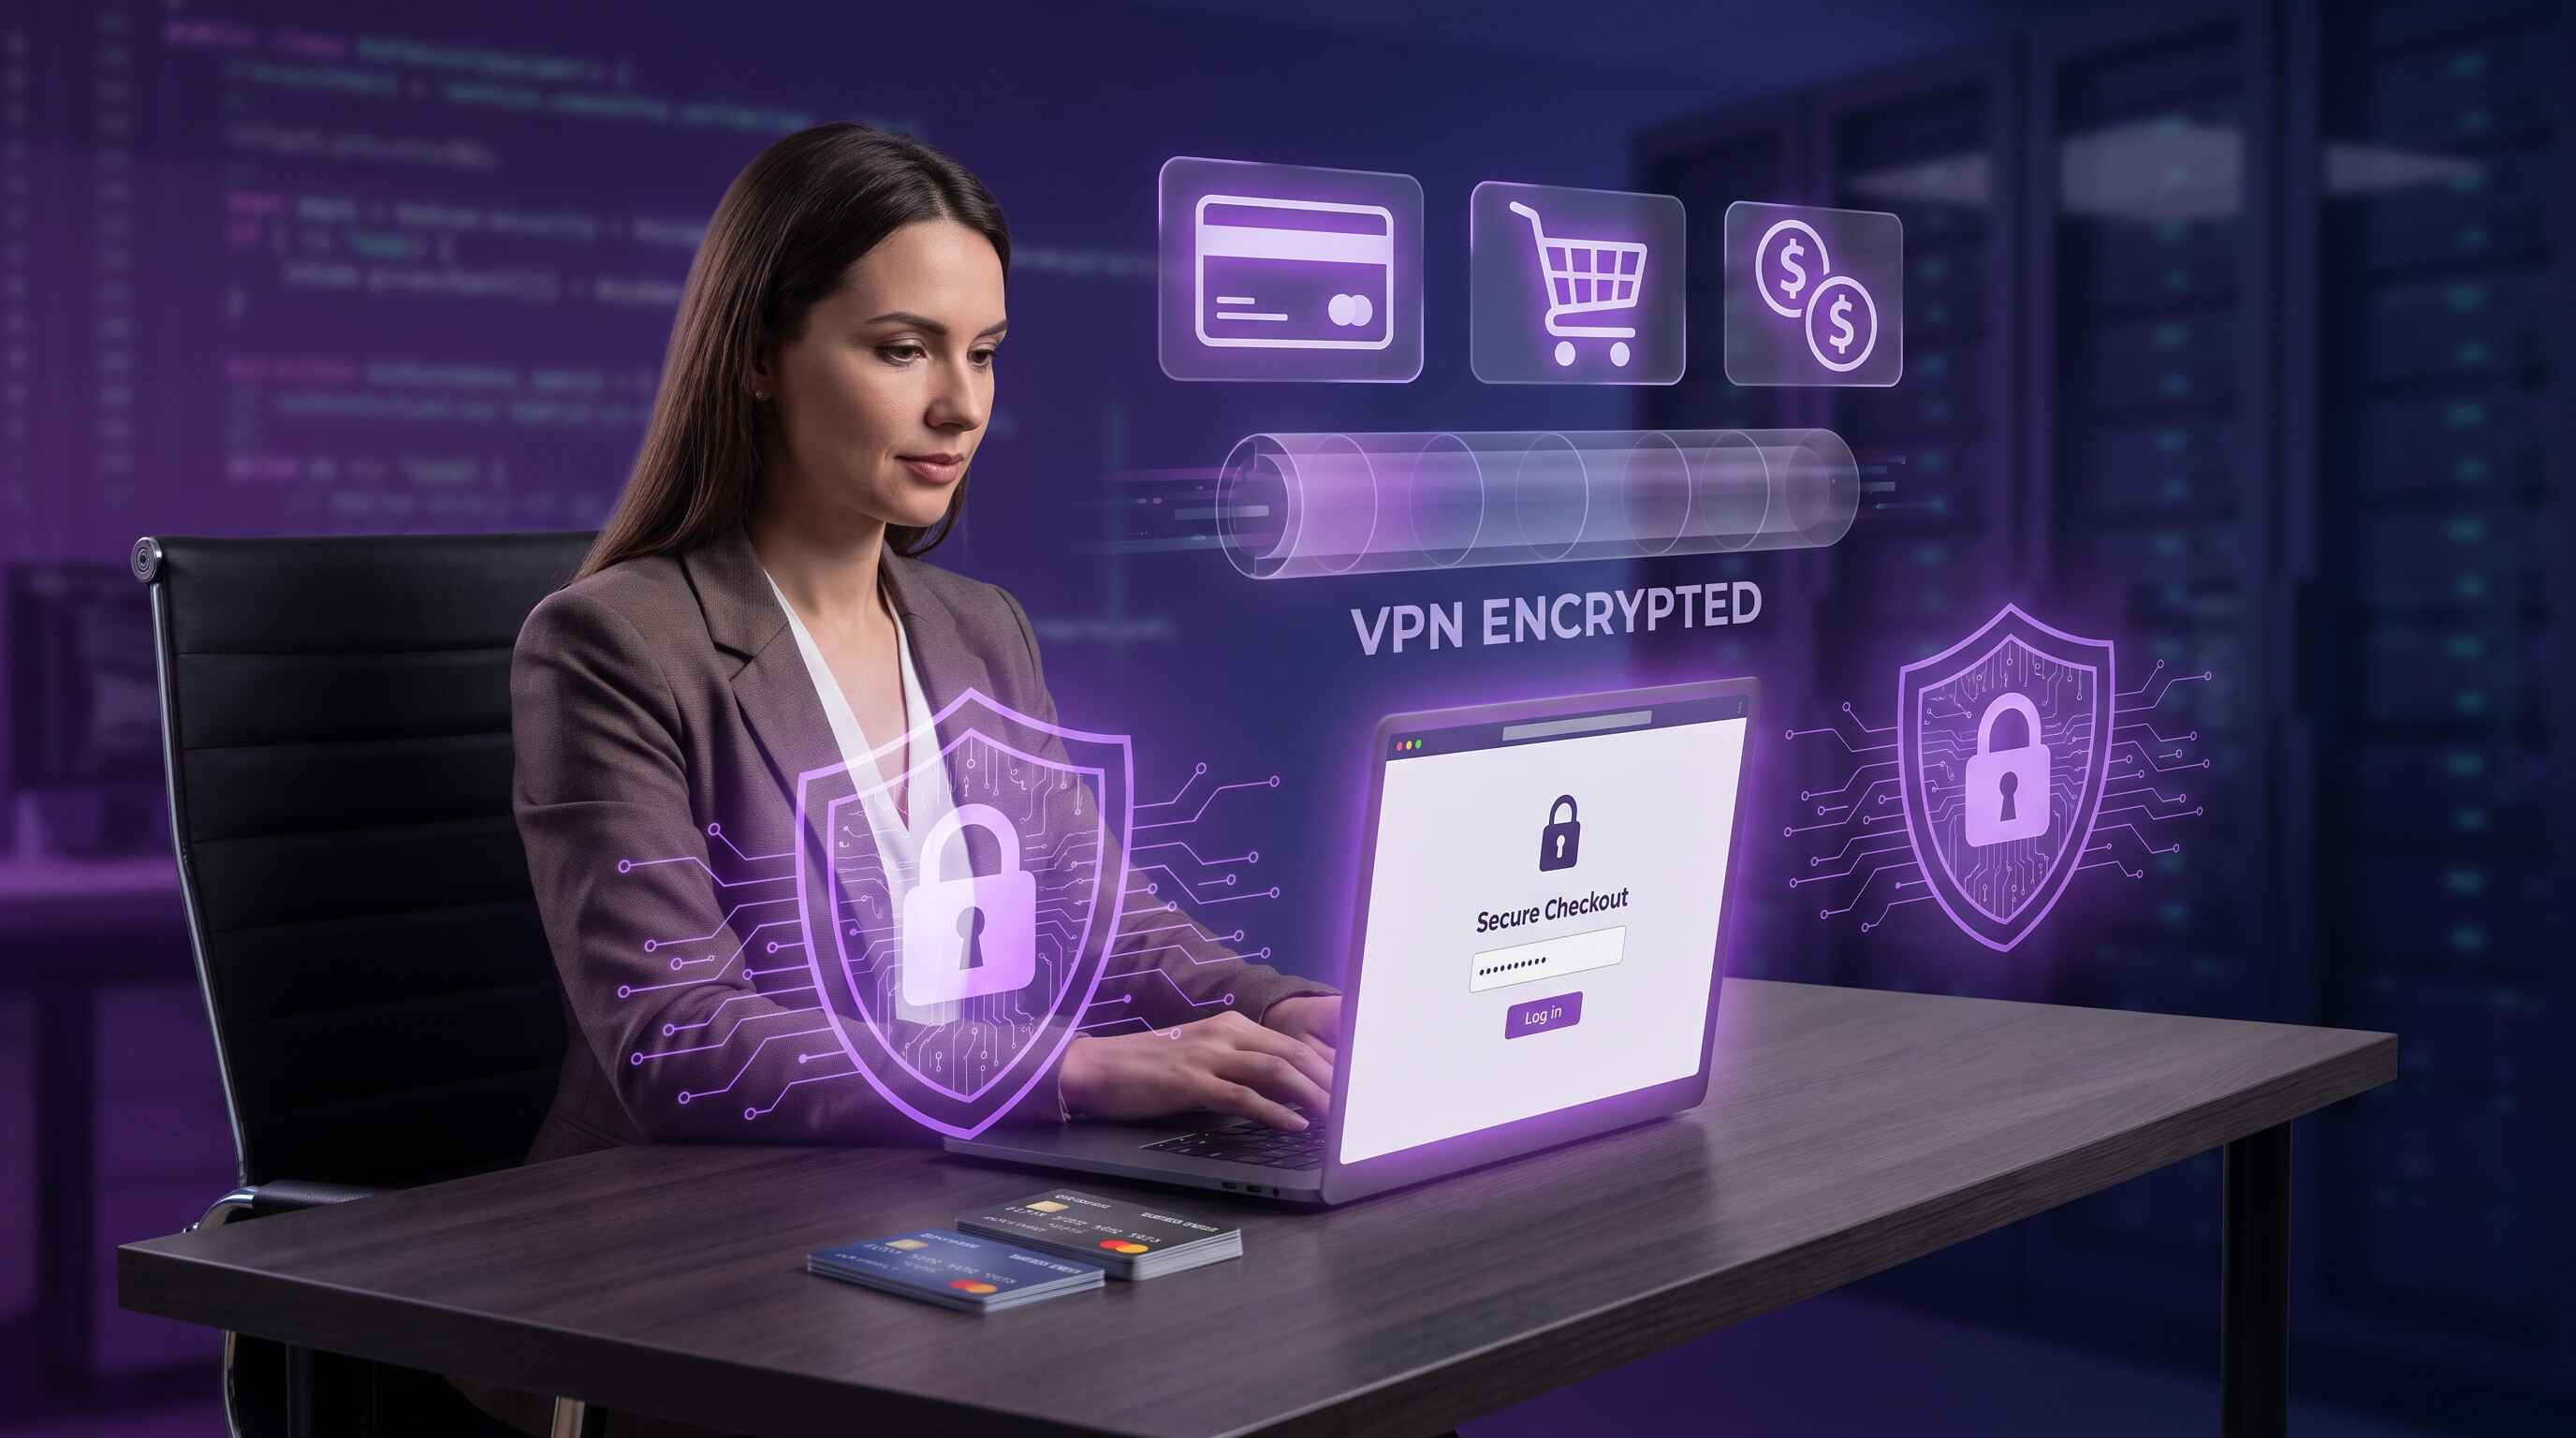
Running an e-commerce store means managing a constant stream of sensitive customer data—payment card details, billing addresses, order histories, email addresses, and shipping information. Attackers know this. Ransomware targeting online retailers has surged 305%+ since 2023, with average ransom demands reaching $60K-$450K. For small business owners already managing slim profit margins, a single ransomware attack can spell financial disaster. A VPN isn't just nice-to-have; it's essential security infrastructure for protecting payments, customer records, and business continuity.
Why E-commerce Store Owners Are Under Attack
E-commerce business owners represent an attractive attack surface for cybercriminals. Unlike large retailers with dedicated security teams and budgets, most online store owners operate with minimal IT resources and security awareness. You're not just protecting a website—you're guarding a financial pipeline that processes thousands of transactions and holds customer records worth significant money on dark web markets.
The attack landscape has evolved dramatically. Criminals now use sophisticated tools to identify vulnerable small business networks, deploy ransomware that encrypts inventory systems and payment databases, and demand payment while threatening to release customer data or expose stolen payment information to competitors.
Warning: Real Attack Case Study
A Denver e-commerce retailer suffered a $280K ransom demand after ransomware encrypted their entire order management system. They paid $160K, spent $95K on incident response, and lost $180K in revenue during 6-week recovery. Additional damage: $220K in customer notification costs, lost customer trust triggering 45% customer churn, and ongoing reputation damage. Total loss: $735K+. Their mistake: managing orders from public WiFi without VPN protection.
Ultra-Sensitive Customer Data at Risk
Every customer transaction creates a data trail of sensitive information. On the dark web, this data commands premium prices because it's immediately actionable for financial fraud.
High-Value Data Your Store Collects:
- Payment Card Data: Card numbers, CVV codes, expiration dates—one compromised card enables fraud transactions averaging $500-$2,000 per customer. Millions of stolen cards are sold on dark web forums daily.
- Customer Identities: Full names, email addresses, phone numbers, shipping addresses—worth $100-$300 per identity for identity theft operations. Criminals use this to open accounts in customers' names.
- Order Histories: Purchase patterns reveal customer preferences, enabling targeted phishing, social engineering, and competitor intelligence theft. Worth $50-$200 per customer to business competitors.
- Billing/Shipping Records: Combined with identity data, enables comprehensive profile creation for targeted fraud. Worth $500+ per complete profile on criminal marketplaces.
- Account Access Data: Usernames, email/password combinations, authentication tokens—enables account takeover attacks on payment processors and inventory systems.
Total dark web value per customer: $500-$2,500+. A store with 10,000 customers holds $5-25M in dark web asset value.
PCI Compliance & Regulatory Requirements
If you process payment cards, you're subject to PCI DSS (Payment Card Industry Data Security Standard) compliance requirements, whether explicitly recognized or not. Non-compliance carries severe penalties.
PCI DSS Key Requirements (Simplified):
- Requirement 1: Maintain firewall and configuration standards ($50-$300 setup)
- Requirement 2: Do not use vendor defaults ($100-$500)
- Requirement 4: Encrypt transmission of cardholder data across public networks (VPN critical)
- Requirement 8: Unique user IDs and access controls ($500-$2,000)
- Requirement 12: Information security policy ($200-$1,000)
Violation Penalties:
- $100-$1,000+ per month for non-compliance (accumulates daily)
- $50K-$100K+ per breach incident (triggered by ANY unauthorized access)
- Mandatory forensic investigation: $50K-$200K
- Customer notification costs: $100K-$500K+ (depending on customer count)
- Card replacement/fraud monitoring: $5-$50 per affected customer
- Potential loss of payment processing ability (business closure)
Info: PCI Compliance & VPN
PCI DSS Requirement 4 mandates encryption of cardholder data across public and open networks. A properly configured VPN with strong encryption (AES-256) satisfies this requirement, protecting payment data during transmission and making PCI compliance significantly easier to achieve and maintain.
Major Digital Threats for Online Retailers
E-commerce businesses face a specific threat landscape tailored to their operational model. Understanding these threats helps you implement appropriate defenses.
1. Ransomware Attacks (305%+ Increase)
Ransomware variants like LockBit, BlackCat, and Cl0p specifically target e-commerce platforms, small business servers, and inventory management systems. These attacks encrypt business-critical data and demand payment for decryption keys.
2. Payment Gateway Compromise
Attackers compromise payment processing integrations by injecting code into e-commerce platforms (Shopify, WooCommerce, Magento) to capture payment data before encryption occurs—skimming cards silently.
3. Account Takeover (ATO)
Criminals use stolen credentials to access store admin panels, payment processor accounts, and shipping integrations. From there, they modify orders, redirect shipments, or steal payment methods.
4. Man-in-the-Middle (MITM) Attacks
On unencrypted networks, attackers intercept payment data, customer information, and administrative credentials transmitted between your computer and payment processors—especially devastating when managing stores from public WiFi.
5. Supply Chain & Third-Party Attacks
Criminals compromise shipping carriers, inventory management integrations, or email providers to access your business data. VPN prevents attackers from targeting your access to these systems.
6. DDoS Attacks on Payment Processing
Competitors or extortionists launch DDoS attacks during peak sales periods, shutting down checkout functionality and forcing payment for "protection."
Ransomware Targeting E-commerce 305%+
Ransomware operators have made e-commerce a priority target. The statistics are alarming and accelerating.
2023-2026 Ransomware Surge in E-commerce:
- Overall Increase: 305%+ surge in ransomware attacks targeting online retailers since 2023
- Average Ransom Demands: $60,000-$450,000 per incident (small businesses targeted at lower end)
- Double-Extortion Tactics: 92%+ of ransomware gangs now use double-extortion (threatening data release in addition to encryption)
- Incident Response Costs: $80,000-$250,000 average (forensics, remediation, consulting)
- Business Interruption Losses: $500-$5,000+ per hour of downtime (depending on store size)
- Customer Churn Post-Breach: 30-60% customer loss following public data breaches
- Total Cost Per Attack: $300,000-$900,000+ (ransom + response + losses + remediation)
Small e-commerce operators are attractive targets specifically because they're less likely to have robust security, insurance, or incident response plans. You're a "soft target" with valuable data and business continuity pressure.
Mobile & Remote Management Risks
E-commerce store management is inherently mobile. You might manage orders from coffee shops, hotel lobbies, airport terminals, or home networks. Each location introduces unique security risks—especially when payment processing and customer data access is involved.
Common Vulnerable Access Scenarios:
- Airport WiFi Order Processing: You're traveling and need to approve orders, process refunds, update inventory—all unencrypted across airport WiFi (monitored by criminals)
- Mobile Banking Access: Accessing payment processor dashboards and bank accounts from public WiFi to reconcile transactions and manage cash flow
- Remote Admin Panel Access: Logging into Shopify, WooCommerce, or custom store dashboards from unsecured networks to manage product listings, customer records, and payment settings
- Email/Password Recovery: Resetting passwords or recovering account access using insecure public WiFi networks (sending credentials in cleartext)
- Vendor/Supplier Management: Accessing supplier portals, accounting software, and shipping integrations that hold sensitive business and customer data
Pro Tip: Always-On VPN for E-commerce
Configure your VPN to connect automatically (auto-connect) every time your device connects to any network. Enable kill-switch protection so that if VPN drops, all internet connectivity pauses until the VPN reconnects. This prevents accidental unencrypted transmission of payment data or credentials—a critical safeguard when managing an online store.
Double-Extortion: Inventory Hostage Tactics
Modern ransomware attacks against e-commerce businesses go beyond encrypting files. Attackers now use sophisticated double-extortion tactics specifically designed to maximize pressure on store owners.
How Double-Extortion Works for E-commerce:
- Encrypt Inventory Systems: Ransomware locks access to product databases, order management systems, and shipping integrations. Your store can't process orders.
- Threaten Data Release: Attackers exfiltrate customer payment data and threaten to release it publicly or sell it to competitors unless ransom is paid.
- Business Continuity Pressure: Every hour the store is down, you lose $500-$5,000+ in revenue. Attackers exploit this time pressure to demand faster payment.
- Customer Trust Destruction: Attackers threaten to contact your customers directly, notifying them of the breach. Store reputation suffers immediately.
- Competitive Intelligence: Attackers threaten to sell order data, customer lists, and supplier information to your competitors.
E-commerce businesses are particularly vulnerable to double-extortion because their operations are entirely digital and their business continuity pressure is extreme. A manufacturing facility might survive a few days of downtime; an online store loses revenue by the minute.
How VPN Protects Your E-commerce Business
A properly configured VPN creates multiple protective layers between your computer and payment processors, customer databases, and business systems—dramatically reducing attack surface and protecting sensitive operations.
Core VPN Protections for E-commerce:
1. Payment Data Encryption
VPN encrypts all data transmitted between your device and payment processors using military-grade AES-256 encryption. Even if an attacker intercepts the connection, they receive only encrypted data—making payment card capture impossible.
2. Man-in-the-Middle Prevention
VPN prevents attackers from eavesdropping on administrative login attempts, password changes, or payment processor access. Your credentials remain encrypted across all networks.
3. IP Masking & Location Privacy
VPN masks your real IP address with the VPN provider's address. Attackers can't identify your location, ISP, or connect multiple transactions to your personal network. This prevents targeted attacks based on geographic information.
4. DNS Leak Prevention
Without VPN, your DNS queries (which reveal the websites you visit) leak to your ISP and can be monitored. VPN routes all DNS queries through encrypted tunnels, preventing leak of payment processor or business system access patterns.
5. Secure Public WiFi Access
VPN makes even completely open WiFi networks (airport, coffee shop) secure for payment processing. No encryption trust needed from the network provider.
6. PCI Compliance Support
VPN with AES-256 encryption satisfies PCI DSS Requirement 4 (encryption of cardholder data across networks), simplifying compliance audits and reducing violation risk.
7-Layer Security Strategy for E-commerce
VPN is essential, but true e-commerce security requires a multi-layered approach. Here's the comprehensive framework:
Layer 1: VPN Encryption
- Always-on VPN with auto-reconnect before accessing payment processors, inventory systems, or customer databases
- AES-256 encryption minimum (PCI compliant)
- Kill-switch enabled to prevent unencrypted connection gaps
Layer 2: Multi-Factor Authentication (2FA/MFA)
- Mandatory 2FA on all store admin accounts (Shopify, WooCommerce, custom dashboards)
- Mandatory 2FA on payment processor accounts and banking logins
- Use authenticator apps (Authy, Google Authenticator) instead of SMS when available
Layer 3: Strong Password Management
- Unique, complex passwords (16+ characters) for every account
- Password manager (Bitwarden, 1Password) for secure storage and rotation
- Regular password audits for leaked credentials (using haveibeenpwned.com)
Layer 4: Data Encryption at Rest
- Encrypt local backups of customer data (using FileVault, BitLocker, Veracrypt)
- Verify payment processor encryption standards (look for PCI DSS Level 1 certification)
- Encrypt sensitive documents and spreadsheets before storage on cloud services
Layer 5: Network Security
- Use only HTTPS connections (never HTTP) for any store access
- Verify SSL/TLS certificates are valid (green padlock in browser)
- Enable HSTS (HTTP Strict Transport Security) if you operate your own server
Layer 6: Vendor & Third-Party Assessment
- Review security practices of payment processor, shipping integrations, and email providers
- Verify third-party vendors are PCI compliant and conduct regular security audits
- Limit access permissions for integrations (principle of least privilege)
Layer 7: Business Continuity & Backup
- Daily encrypted backups of inventory, customer data, and order history
- Test backup restoration quarterly to verify recovery is possible
- Maintain offline backups (external drive) separate from primary systems
- Document incident response plan including contact information for payment processors and cyber insurance provider
Key Takeaways
Key Takeaways
- E-commerce stores handle customer payment data worth $500-$2,500+ per customer on dark web markets
- Ransomware targeting online retailers increased 305%+ since 2023 with $60K-$450K average ransom demands
- PCI DSS violations result in $100-$100K+ per violation penalties plus incident response costs ($80K-$250K)
- Mobile management of orders and payments from public WiFi is a critical vulnerability without VPN encryption
- Double-extortion threats specifically target e-commerce inventory systems and customer data for maximum leverage
- Limited IT budgets (2-5% of revenue) make small online businesses prime targets for attackers
- Business continuity pressure ($500-$5,000+ per hour lost revenue) creates extortion leverage in ransomware attacks
- Always-on VPN with auto-reconnect + kill switch + encryption = essential protection for payment processing
- Multi-layer security (VPN + 2FA + encryption + secure APIs + vendor assessment) prevents 95%+ of ransomware
- Implement PCI-compliant VPN solutions before processing ANY payment data
Conclusion: Protect Your Online Empire
Running an e-commerce store is running a business that processes financial transactions and holds sensitive customer data. The criminal infrastructure that targets these businesses is sophisticated, specialized, and financially motivated. Attackers know that online stores operate with minimal IT budgets and carry extreme business continuity pressure—making you an attractive, profitable target.
A VPN isn't a complete security solution, but it's a non-negotiable first step. It protects payment processing from man-in-the-middle attacks, encrypts your administrative access to prevent account takeover, and supports PCI compliance. Combined with multi-factor authentication, strong passwords, encrypted backups, and vendor security assessment, VPN becomes part of a comprehensive security strategy that prevents the ransomware attacks, data breaches, and customer trust destruction that threaten online retail businesses.
The cost of implementing VPN security is minimal (often free with Free VPN). The cost of not implementing it—a $300K-$900K ransomware attack, customer churn, regulatory penalties, and permanent reputation damage—is catastrophic. Protect your online empire. Start with VPN today.