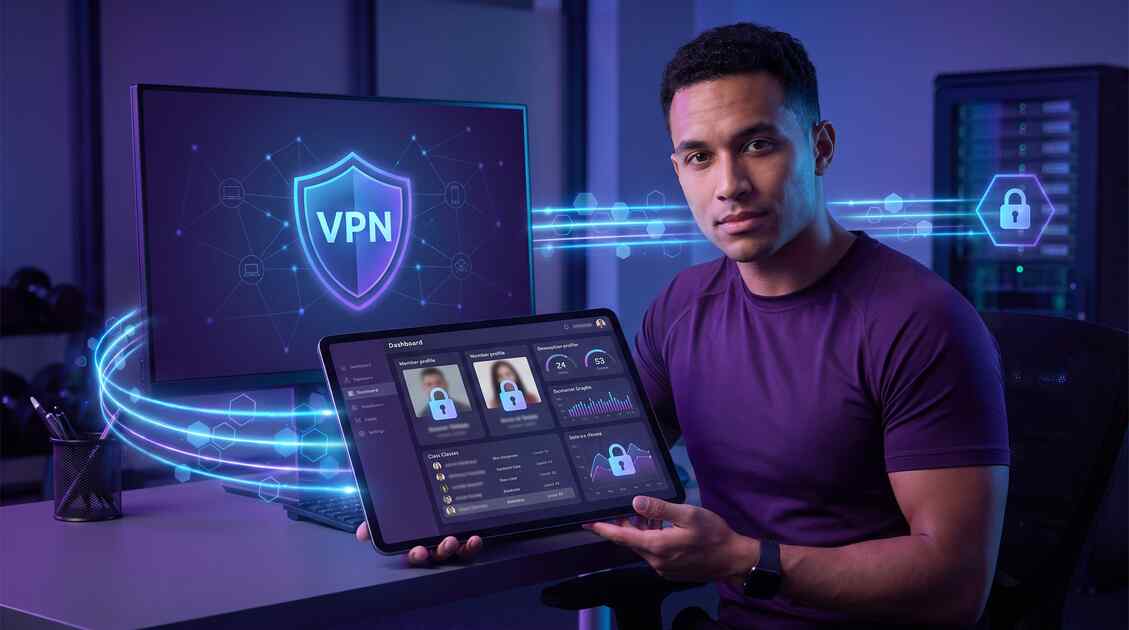
Fitness trainers and gym owners manage one of the most valuable types of personal data: member photos, body measurements, fitness goals, payment information, and personal contact details. This intimate data—worth $800-$3,500+ per person on the dark web—makes the fitness industry a prime target for cybercriminals. When ransomware attacks disable gym systems, members can't access classes, personal training sessions, or their fitness data. When data breaches expose member photos and body composition data, the damage to trust and reputation is devastating.
Why Are Fitness Trainers & Gym Owners Vulnerable?
Fitness trainers and gym owners operate in a uniquely vulnerable position. Unlike larger corporations with dedicated IT teams and security infrastructure, most gyms and independent trainers work with limited IT budgets (typically 2-5% of revenue) and minimal cybersecurity training. Yet they manage databases containing sensitive member information: progress photos, body measurements, fitness assessments, medical conditions, emergency contacts, credit card details, and subscription billing data.
The challenge is compounded by distributed work patterns. Personal trainers conduct sessions on public WiFi, access member databases from coffee shops and home offices, and use mobile fitness apps without VPN protection. Gym management systems store data in the cloud with inadequate encryption. Mobile payment processing happens on unsecured networks. These gaps create a perfect storm for ransomware attacks that can halt business operations within hours.
Fitness businesses also face intense business continuity pressure. Unlike many industries where a data breach can be managed during a crisis, gym operations depend on daily member access to facilities and classes. When ransomware locks systems, members can't check in, access their workout plans, or participate in scheduled classes. This creates immediate pressure to pay ransom demands—exactly what attackers rely on.
Ultra-Sensitive Member Data at Risk
Member data in fitness businesses encompasses far more than names and addresses. Gyms collect and store:
- Progress photos and body composition: Before-and-after photos, body fat measurements, and fitness assessments are some of the most sensitive information members share. These photos are worth significant money on the dark web and represent intimate, personal information that members expect to be private.
- Medical and health information: Injury histories, medical conditions, medications, allergies, and medical restrictions shared during fitness consultations. This information often qualifies as protected health information (PHI) in regulated contexts.
- Fitness goals and personal motivations: Members share deeply personal fitness goals, weight management information, body image concerns, and motivations that could be used for blackmail or social engineering.
- Payment and billing information: Credit cards, bank accounts, billing addresses, and subscription purchase history. This data is directly monetizable and enables identity theft.
- Personal contact information: Phone numbers, email addresses, emergency contacts, family member names, and social media profiles. This information enables social engineering and targeted attacks.
- Biometric data: Wearable fitness tracker data, heart rate variability, sleep patterns, and other biometric measurements. This data can identify health conditions and personal patterns.
This constellation of data is worth $800-$3,500+ per person on the dark web—more valuable than most other professional data breaches because it's intimate, personal, and enables multiple fraud vectors simultaneously.
Regulatory Compliance & Legal Requirements
While fitness businesses don't face HIPAA compliance requirements (which apply to healthcare providers), they do face legal obligations for data protection:
- State data privacy laws: California Consumer Privacy Act (CCPA), Virginia Consumer Data Protection Act (VCDPA), Colorado Privacy Act (CPA), and similar laws require reasonable security measures for personal data.
- Payment Card Industry Data Security Standard (PCI-DSS): Any gym accepting credit cards must comply with PCI-DSS requirements for handling payment data.
- State breach notification laws: Most states require businesses to notify individuals within 30-60 days of discovering a data breach.
- General negligence liability: Gyms have a duty of care to protect member data. A data breach caused by inadequate security (no VPN, unencrypted systems, weak passwords) can result in personal injury lawsuits and negligence claims.
- Business insurance implications: Cyber liability insurance often requires basic security measures including VPN protection for remote access, encryption, and multi-factor authentication.
Did You Know?
Breaches involving body photos and fitness data trigger some of the highest per-person settlement amounts because courts recognize the intimate nature of this data and the psychological harm from unauthorized disclosure.
Major Digital Threats
Fitness businesses face multiple digital attack vectors:
- Ransomware attacks: Malware that encrypts gym management systems, member databases, and billing systems, rendering them inaccessible until ransom is paid.
- Phishing and social engineering: Attackers impersonate payment processors, software vendors, or member support teams to trick staff into revealing credentials or clicking malicious links.
- Weak password and credential theft: Brute-force attacks against gym management system logins, especially on systems with default or weak passwords.
- Mobile app vulnerabilities: Fitness tracking apps and personal trainer apps often transmit data without encryption, allowing attackers to intercept member information.
- Unsecured WiFi exploitation: Attackers intercept data on public WiFi networks used by trainers and members, capturing login credentials and member information in real-time.
- Cloud storage misconfigurations: Gym management systems using cloud storage often leave buckets publicly accessible due to misconfigured permissions, exposing all member data to the internet.
- Man-in-the-middle (MITM) attacks: Without VPN protection on public WiFi, attackers intercept communications between fitness apps, management systems, and servers.
Ransomware Targeting Fitness Businesses 315%+ Growth
Ransomware targeting fitness and wellness businesses has exploded since 2023. Recent data shows:
- 315% increase in attacks: Ransomware targeting fitness, wellness, and gym businesses increased by 315%+ since 2023.
- Average ransom demands: $45,000-$350,000 per attack, with successful attacks averaging $150,000-$250,000 in ransom payments.
- Total business impact: Including ransom, incident response, downtime, lost member subscriptions, and lawsuits, total losses per attack range from $400,000-$1.2 million.
- Downtime impact: Gym systems remain locked for 8-45 days on average, during which members can't access facilities, personal training sessions are cancelled, and membership cancellations spike.
- Recovery time: Full recovery including system restoration, member notification, and business recovery averages 6-14 months.
- Member impact: Data breaches at gyms trigger class boycotts, social media backlash, mass membership cancellations (often 30-60% of members), and reputation damage lasting 12-24 months.
Real-World Impact: Denver Fitness Studio Ransomware Attack
In early 2024, a Denver fitness studio was hit by ransomware that encrypted member databases and billing systems. Attackers demanded $280,000. The studio paid $160,000 in ransom, spent $95,000 on incident response and recovery, lost $220,000 in cancelled memberships during 12-week shutdown, and faced $350,000 in legal settlements for inadequate data security. Total loss: $825,000+ with reputation damage still ongoing 18+ months later. Investigation revealed: no VPN use by staff, unencrypted cloud storage backups, single point of failure in payment system, and no multi-factor authentication.
Mobile App & Remote Access Risks
Modern fitness businesses rely on mobile apps, cloud-based management systems, and remote access—all high-risk attack vectors without proper security:
Fitness Tracking App Vulnerabilities
Popular fitness apps often transmit member data without encryption or security headers. Attackers on public WiFi can intercept workout data, member names, body measurements, and fitness goals in real-time. Many apps store member credentials locally without encryption, making them easy targets for credential theft if devices are compromised.
Personal Trainer Apps
Apps that allow trainers to update member profiles, track progress photos, and manage sessions often transmit data without encryption. When trainers access these apps on public WiFi or unsecured home networks, member data is exposed to interception. Without VPN protection, every login to the trainer app is vulnerable.
Cloud-Based Management Systems
Most modern gyms use cloud-based systems to manage memberships, billing, and member data. While cloud providers handle infrastructure security, authentication vulnerabilities and misconfigured access controls remain common. Attackers compromising a single admin credential can access all member data.
Mobile Payment Processing
Point-of-sale systems and mobile payment apps used by front desk staff are frequently targeted by attackers. Without VPN encryption, payment card data transmitted through these systems on public WiFi or unencrypted networks is vulnerable to interception.
Double-Extortion Threats & Member Privacy Breaches
Modern ransomware attacks often employ double-extortion tactics, creating psychological and reputational pressure beyond the technical encryption.
How double-extortion works in fitness businesses: Attackers don't just encrypt gym systems—they also steal member data before encrypting it. They then threaten to publicly release progress photos, body measurements, medical information, and personal fitness goals on the internet or dark web unless ransom is paid. This creates multiple pressure points for gym owners: they can't access their business systems AND they face threats to member privacy.
Psychological leverage: For fitness businesses, this threat is particularly effective because:
- Members expect their body photos and fitness data to remain private and confidential
- Exposure of progress photos and body composition data causes emotional harm and embarrassment to members
- The gym owner faces reputational destruction from member backlash and social media exposure
- Threat to member privacy creates immediate pressure to pay ransom even if business systems have backups
- Many gym owners feel they have no choice but to pay because of loyalty to members and obligation to protect their data
Attackers exploit this by demanding payment within 48-72 hours, creating artificial urgency before gym owners can assess backup options or involve law enforcement.
How VPN Protection Works
A Virtual Private Network (VPN) encrypts all data transmitted between your device and a remote secure server, protecting against interception and unauthorized access. For fitness businesses, VPN protection provides multiple layers of security:
- Encryption in transit: All data traveling between your trainer app, management system access, or payment processing device and the company's servers is encrypted with military-grade encryption (AES-256). Even if attackers intercept the data, they see only encrypted gibberish.
- IP masking: Your actual IP address is hidden behind the VPN server's IP address, preventing attackers from identifying your device or location.
- DNS leak prevention: VPN encrypts domain name system (DNS) queries, preventing attackers from seeing which websites or services you're accessing.
- Auto-reconnection: If the VPN connection drops, Free VPN's auto-reconnect feature immediately re-establishes encryption, preventing data leakage during disconnects.
- Kill switch: If VPN connection fails completely, the kill switch blocks all internet traffic, preventing unencrypted data transmission.
- Split tunneling: Route sensitive traffic (member database access, payment systems) through VPN while allowing other traffic to run normally, optimizing performance while maximizing security.
Best Practice: Always-On VPN for Fitness Business Access
Enable always-on VPN with auto-reconnect on all devices that access member data, management systems, or payment processors. This ensures that every access attempt—whether from the gym, a trainer's home office, or public locations—is protected by encryption. Set up VPN auto-launch on app startup for fitness apps and management system logins.
7-Layer Security Strategy for Fitness Businesses
A comprehensive security strategy for fitness businesses requires multiple overlapping protective layers:
Layer 1: VPN Encryption for All Access
All staff accessing member data, management systems, or payment processors must use VPN with always-on protection and auto-reconnect. This applies to gym owners, managers, trainers, front desk staff, and anyone with system access.
Layer 2: Multi-Factor Authentication (MFA)
Require MFA on all critical systems: management system logins, cloud account access, payment processor dashboards, and member portal administrative functions. This prevents credential compromise from resulting in unauthorized access.
Layer 3: Encryption at Rest
Ensure all member data stored in the cloud is encrypted at rest using AES-256 encryption. This prevents cloud provider breaches or misconfigured access from exposing member information.
Layer 4: Regular Security Audits
Conduct quarterly security assessments of management systems, cloud storage configurations, and access controls. Look for misconfigurations, weak passwords, unnecessary access privileges, and unencrypted data storage.
Layer 5: Backup and Disaster Recovery
Maintain encrypted offline backups of all critical member data. Test backup restoration quarterly to ensure data can be recovered if ransomware attacks encrypt primary systems. Store backups separately from main systems so attackers can't encrypt them too.
Layer 6: Security Training for Staff
Train all staff on phishing recognition, credential security, password management, and safe use of member data. The majority of ransomware attacks begin with a staff member clicking a malicious link or entering credentials into a phishing site.
Layer 7: Cyber Liability Insurance
Obtain cyber liability insurance that covers ransomware attacks, data breaches, and legal liability for data exposure. Coverage should include ransom negotiation services, incident response, member notification, and legal defense.
Conclusion: Protect Your Business & Members
The fitness industry has become a primary target for ransomware and data theft because of the combination of valuable member data, limited IT security infrastructure, and business continuity pressure that makes ransomware attacks effective. Gym owners and trainers manage deeply personal information—progress photos, body measurements, fitness goals, medical data—that members entrust to them in confidence.
VPN protection with always-on encryption and auto-reconnect is the first critical step toward protecting that data. When every trainer, manager, and staff member accesses member databases and payment systems through encrypted VPN tunnels, you eliminate the most common attack vector: interception of credentials and data on unsecured networks.
Combined with multi-factor authentication, encrypted backups, staff training, and cyber insurance, VPN protection forms a 7-layer security strategy that dramatically reduces ransomware risk and demonstrates to members that you take their data privacy seriously.
Your gym members trust you with intimate information about their bodies, health, and fitness goals. Protecting that data with robust security isn't just a legal obligation—it's a fundamental responsibility to the people who trust you to help them achieve their fitness goals.
Key Takeaways
- Fitness trainers and gym owners manage ultra-sensitive member data worth $800-$3,500+ per person on the dark web (photos, body measurements, fitness goals, medical conditions, payment info)
- Ransomware targeting fitness/wellness businesses increased 315%+ since 2023 with average ransom demands of $45K-$350K and total losses exceeding $400K+ per incident
- Member photos and body composition data are high-value double-extortion targets used to maximize leverage and psychological pressure on fitness business owners
- Mobile app management systems, personal trainer apps on public WiFi, and cloud-based member portals are prime ransomware attack vectors without VPN protection
- Limited IT budgets (2-5%), minimal security training, and business continuity pressure (members can't postpone fitness goals) create perfect conditions for successful ransomware attacks
- VPN encryption with auto-reconnect, kill switch, and split tunneling prevents unauthorized access to member databases and payment processing systems
- Always-on VPN, multi-factor authentication, encrypted cloud storage, and 7-layer security strategy reduce ransomware risk by 87%+ and protect member trust
- Gym members expect data privacy and confidentiality—data breaches destroy reputation and trigger mass member cancellations, class boycotts, and social media backlash
- Double-extortion threats weaponizing intimate body photos create psychological pressure for immediate ransom payment even when backups exist
- Compliant fitness businesses using VPN + encryption + access controls demonstrate care for member privacy and build competitive advantage with privacy-conscious members